Cybersecurity Services

Cybersecurity services that protect your data, cloud and people

Nxerra helps growing and enterprise teams find their weak spots, close them and keep watch. From security assessments and penetration testing to Microsoft-native monitoring, identity and compliance, we build defences that fit the way your business actually works.

  • Zero Trust
  • Penetration testing
  • Cloud security
  • Microsoft Security
  • Compliance readiness
  • 2022 Year Nxerra was founded
  • 1,500 Projects delivered
  • 98% Customer satisfaction
  • 3 Development centers: India, USA, Australia
Why security, why now

Security is an engineering discipline, not a checklist

The threat landscape keeps moving. Every new cloud service, remote device and third-party integration widens the area you have to protect, and attackers only need one gap.

Our cybersecurity services bring assessment, engineering and monitoring together, so you reduce real risk instead of just collecting reports. The result is protection that supports how you grow, rather than slowing it down.

Core security capabilities

  • Zero Trust design with identity-first access and network segmentation
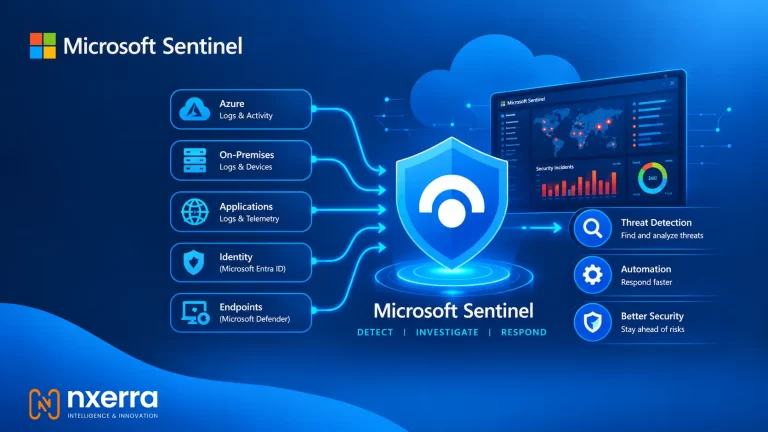
  • Threat detection and response built on Microsoft Sentinel and Defender
  • Continuous vulnerability management with prioritised, tracked fixes
  • Data protection that follows your information across devices and cloud
  • Audit-ready evidence for ISO 27001, SOC 2, GDPR, HIPAA and PCI DSS
What we do

Our enterprise cybersecurity services

Every new endpoint, cloud integration and partner adds risk. Our services are built to find that risk, contain it and keep it contained.

01

Security Consulting & Roadmap

We review your current security posture, spot structural gaps and turn them into a practical multi-year plan tied to your business goals.

  • Security posture and architecture review
  • Prioritised roadmap with owners and budgets
02

Vulnerability Assessment & Penetration Testing

Our testers go beyond automated scanners. They chain real attack paths and business-logic flaws, then hand your developers clear, repeatable fixes.

  • Web, mobile and API penetration testing
  • Network, cloud and infrastructure testing
03

Cloud Security

Secure Azure, Microsoft 365 and multi-cloud estates by finding misconfigurations, risky permissions and exposed services before attackers do.

  • Cloud posture and identity risk assessment
  • Secure landing zones and workload protection
04

Managed Detection & Response

Continuous monitoring turns raw logs into alerts that matter, with a clear path from detection to containment.

  • Microsoft Sentinel and Defender monitoring, tuning and threat hunting
  • Incident response and forensic investigation support
05

Application Security & DevSecOps

Security checks built into your pipeline catch flaws while they are cheap to fix, not after release.

  • SAST, DAST and dependency scanning in CI/CD
  • Threat modelling and secure code review
06

Identity & Access Management

Identity is the new perimeter. We design access so the right people get the right permissions and attackers get nowhere.

  • SSO, MFA and conditional access with Microsoft Entra ID
  • Privileged access and just-in-time elevation
07

Data Protection & Privacy

Know where sensitive data lives, who can reach it and how it is protected across devices, apps and cloud services.

  • Data classification, DLP and encryption with Microsoft Purview
  • Privacy and data-residency reviews (GDPR, India DPDP Act)
08

GRC & Compliance Readiness

Turn regulations into controls your team can actually run, with evidence collected as part of normal work.

  • Gap assessment and control mapping
  • Policies, risk registers and audit support
09

Security Awareness & Training

People are the most targeted way in. Role-based training and realistic simulations turn them into a strong line of defence.

  • Phishing and social-engineering simulations
  • Executive and board security briefings
10

Resilience & Disaster Recovery

Plan for the day systems fail or are locked by ransomware, then prove that the plan works.

  • Business impact analysis with RTO and RPO targets
  • Immutable backups and recovery testing
11

AI & LLM Security

AI adds new attack surfaces. We test and harden models, prompts and data pipelines before they reach production.

  • Prompt-injection and data-leakage testing
  • AI governance and secure deployment reviews
12

Red & Purple Team Exercises

Simulated adversaries test whether your people, processes and tools can spot and stop a realistic attack.

  • Attack simulations mapped to MITRE ATT&CK
  • Joint purple-team sessions to sharpen detections

See your business the way an attacker does

Book a security assessment and get a prioritised list of the weaknesses worth fixing first, explained in plain language.

Book a security assessment
How we work

Engineering your defence, step by step

Checklists do not stop determined attackers. Our approach builds depth into your architecture and tests every control against realistic attack techniques.

  1. 1

    Discover & map

    We learn what matters most: your critical data, systems and the paths an attacker could take to reach them.

  2. 2

    Assess the gaps

    We test your controls against frameworks like NIST CSF and CIS, and against real attack techniques.

  3. 3

    Plan the fixes

    Findings become a prioritised roadmap that separates quick wins from longer architectural changes.

  4. 4

    Build & harden

    We implement controls with your team: identity, segmentation, secure configuration and monitoring.

  5. 5

    Monitor & improve

    We keep watch, respond to incidents, retest fixes and report progress in plain language.

Industries

Security expertise that fits your sector

Regulations and threat profiles differ from one industry to the next. We bring the context you need to meet the rules that apply to you.

  • BFSI & FinTech

    PCI DSS, payment and fraud-system security

  • Healthcare

    HIPAA, patient data and connected devices

  • E-commerce & Retail

    Checkout security and customer privacy

  • Manufacturing

    OT and ICS segmentation, supplier risk

  • Government & Public Sector

    Framework-aligned controls and resilience

  • Energy & Utilities

    SCADA monitoring and critical infrastructure

  • Telecom

    Subscriber data and network security

  • Education

    Student data and campus identity

  • Logistics

    Fleet, IoT and vendor risk

  • SaaS & Technology

    SOC 2 readiness and secure SDLC

Compliance

Frameworks we help you meet

We help you prepare for, implement and maintain the standards that matter to your customers and regulators.

  • ISO/IEC 27001
  • SOC 2
  • GDPR
  • HIPAA
  • PCI DSS
  • NIST CSF
  • CIS Controls
  • OWASP Top 10
  • ISO 22301
  • India DPDP Act

Certification and attestation are issued by independent auditors. Nxerra supports you in preparing for them.

Why Nxerra

Why teams trust us with their security posture

Innovation needs strong protection. We close the gap between fast product delivery and solid security, so you can adopt cloud and AI with confidence.

  1. 01

    Microsoft-native security expertise

    We work with Microsoft Sentinel, Defender, Entra ID and Purview, so your security tools fit the platforms you already run.

    See our Microsoft Security services
  2. 02

    We fix, not just report

    A long list of findings does not make you safer. Our engineers work with your team to close gaps in code, pipelines and infrastructure, then retest.

  3. 03

    Compliance built into engineering

    We treat compliance as part of the architecture, with automated checks and evidence so you stay audit-ready between audits.

  4. 04

    Zero Trust by design

    Every identity and device is verified, and access is limited to what is needed. If something goes wrong, the damage stays contained.

  5. 05

    Clear, honest communication

    You get plain-language reports, realistic priorities and a team across India, the USA and Australia that stays with you after the report is delivered.

Ready for what is next

Future-ready security capabilities

Static defences fail against modern attackers. These capabilities close the gap between meeting a standard and being genuinely resilient.

Attack Surface Management

Continuous discovery of exposed assets, forgotten subdomains and shadow IT before attackers find them.

Identity Threat Detection

Spot stolen credentials, privilege escalation and suspicious sign-ins that standard access controls miss.

Breach & Attack Simulation

Safe, automated attack scenarios that keep proving your detection and response controls still work.

Software Supply Chain Security

SBOMs, dependency checks and hardened pipelines to protect what you build and what you borrow.

Ransomware-Resilient Recovery

Isolated, tamper-proof backups so you can restore quickly without negotiating.

Post-Quantum Readiness

Inventory your cryptography today and plan a safe path to quantum-resistant standards.

Technology

Platforms and frameworks we work with

We pick tools to fit your existing investments and risk profile, not the other way around.

Microsoft security stack

  • Microsoft Sentinel
  • Defender XDR
  • Microsoft Entra ID
  • Microsoft Purview
  • Microsoft Intune
  • Defender for Cloud

Testing & scanning

  • Burp Suite
  • OWASP ZAP
  • Nessus
  • Nmap
  • Metasploit
  • SonarQube

Cloud & infrastructure

  • Microsoft Azure
  • AWS
  • Google Cloud
  • Kubernetes
  • Terraform
  • Azure DevOps

Frameworks & standards

  • MITRE ATT&CK
  • NIST CSF
  • CIS Benchmarks
  • OWASP
  • ISO 27001
  • Zero Trust
In practice

Typical engagements

Three situations we are often asked to help with. They are illustrative scenarios rather than individual client stories. You can read real projects in our case studies.

Preparing for a first SOC 2 or ISO 27001 audit

The challenge
Customers are asking for certification, but security work has grown informally and nothing is documented.
What we do
Gap assessment, control design, policies, automated evidence collection and support during the audit.
What you get
A working control set and an evidence trail your auditor can follow.

Securing a move to Azure or Microsoft 365

The challenge
The migration expands your attack surface and default settings leave doors open.
What we do
Secure landing zone, hardened identity with conditional access, Defender for Cloud baselines and Sentinel monitoring.
What you get
A secure baseline and full visibility from day one.

Recovering after a phishing or ransomware scare

The challenge
It is unclear what was touched, and there is pressure to restore services fast.
What we do
Containment, investigation, removal of persistence, identity and backup hardening, then retesting.
What you get
A documented root cause, closed gaps and a recovery process that has been tested.

Your security architecture is a business lever. Treat it that way.

Talk to us about how modern identity, cloud and monitoring can speed up your digital plans without adding risk you cannot accept.

Schedule a security briefing
Resources

Latest security insights

View all articles
FAQ

Questions? Look here.

Answers to what businesses ask us most before starting a security project. Can't find yours? We are glad to help.

Ask our experts

We help you understand where your business is exposed, fix the gaps and keep watch. That covers security assessments and penetration testing, cloud and identity security, threat monitoring and incident response, and preparing for compliance frameworks such as ISO 27001, SOC 2 and GDPR.

Start with a risk assessment and a penetration test of your most important systems. It shows what an attacker could realistically reach, and gives you a prioritised list of fixes instead of a generic checklist.

A vulnerability assessment uses scanning tools to find known weaknesses across many systems. Penetration testing goes further: skilled testers try to exploit those weaknesses and chain them together, which shows the real impact on your business.

Yes. We run gap assessments, design and implement the controls, write policies and set up evidence collection. Certification itself is issued by independent auditors, and we support you through that process.

Yes. Microsoft security is a core part of our practice, including Microsoft Sentinel, Defender, Entra ID and Purview. We help with design, deployment, tuning and day-to-day monitoring.

No. Security does not depend on a migration. For older systems we use compensating controls such as network segmentation, virtual patching, tighter access and monitoring, and we can plan a move to the cloud when you are ready.

It depends on scope. A single application can often be tested in a few days to a couple of weeks, while a broader assessment across cloud, network and applications takes longer. We agree scope and timelines with you in writing before work begins.

We are happy to sign an NDA before you share anything sensitive. We agree the scope and rules of engagement in advance, limit access to what is needed and deliver findings through secure channels.

Ready to find your weak points before attackers do?

Tell us what you need to protect. A Nxerra security consultant will contact you within 24 hours.

Chat